After suffering a hard crash, I rebooted and I was thrown into GRUB rescue. From there I was suggested to follow this guide: https://github.com/Mirppc/Grub-Recovery-SUSE
With the help of a few people in the discord server, we managed to follow it to the end. However some steps had to be altered, because the mounting didn’t work.
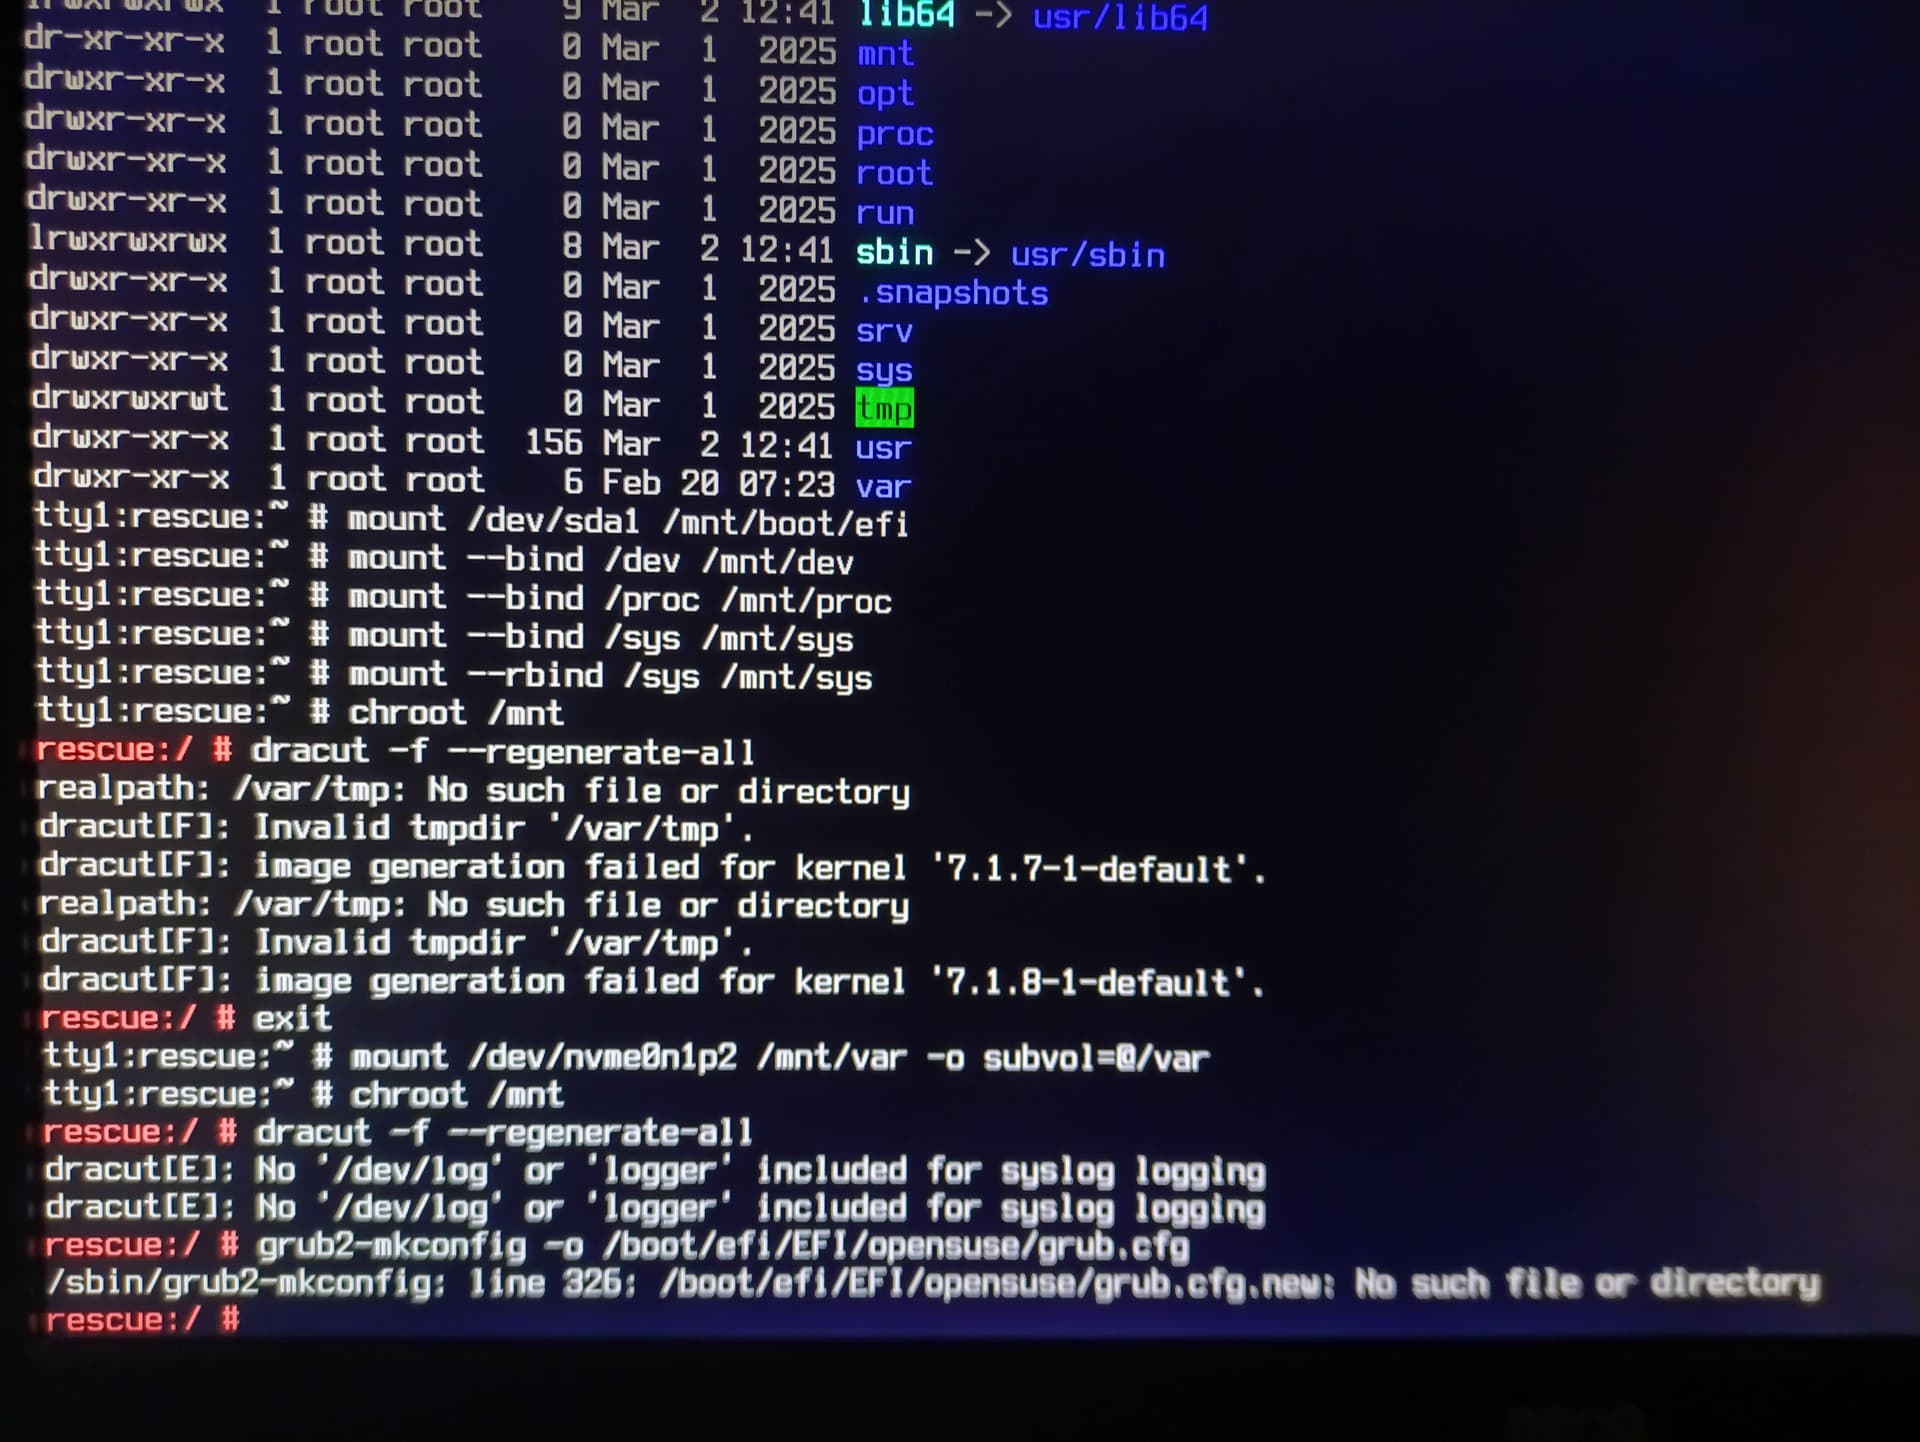
The following commands were entered:
mount /dev/nvme0n1p2 /mnt -o subvol=@/.snapshots/289/snapshot
mount /dev/nvme0n1p1 /mnt/boot/efi
mount --bind /dev /mnt/dev
mount --bind /proc /mnt/proc
mount --bind /sys /mnt/sys
mount --rbind /sys /mnt/sys
mount /dev/nvme0n1p2 /mnt/var -o subvol=@/var
chroot /mnt
dracut -f --regenerate-all
grub2-mkconfig -o /boot/efi/EFI/BOOT/grub.cfg grub2-install /dev/sda (on the first redo, accidentally installed this on the USB drive, which let’s me access the PC for the moment)
grub2-install /dev/nvmen0p1 (on the second redo)
exit, reboot
Doing all that still throws me into the grub rescue mode unless I use the USB drive
That is not the main grub.cfg when traditional boot method, even when EFI. That is what I know and I did edit grub.cfg many times in the past years, not only Tumbleweed. If single OS (per computer, so no multi-boot), that file does not need to be there as a ‘smart enough’ EFI/boot/boot*.efi can find the grub.cfg on the rootfs.
But maybe have a look at (ignore that rEFInd, it is not openSUSE)
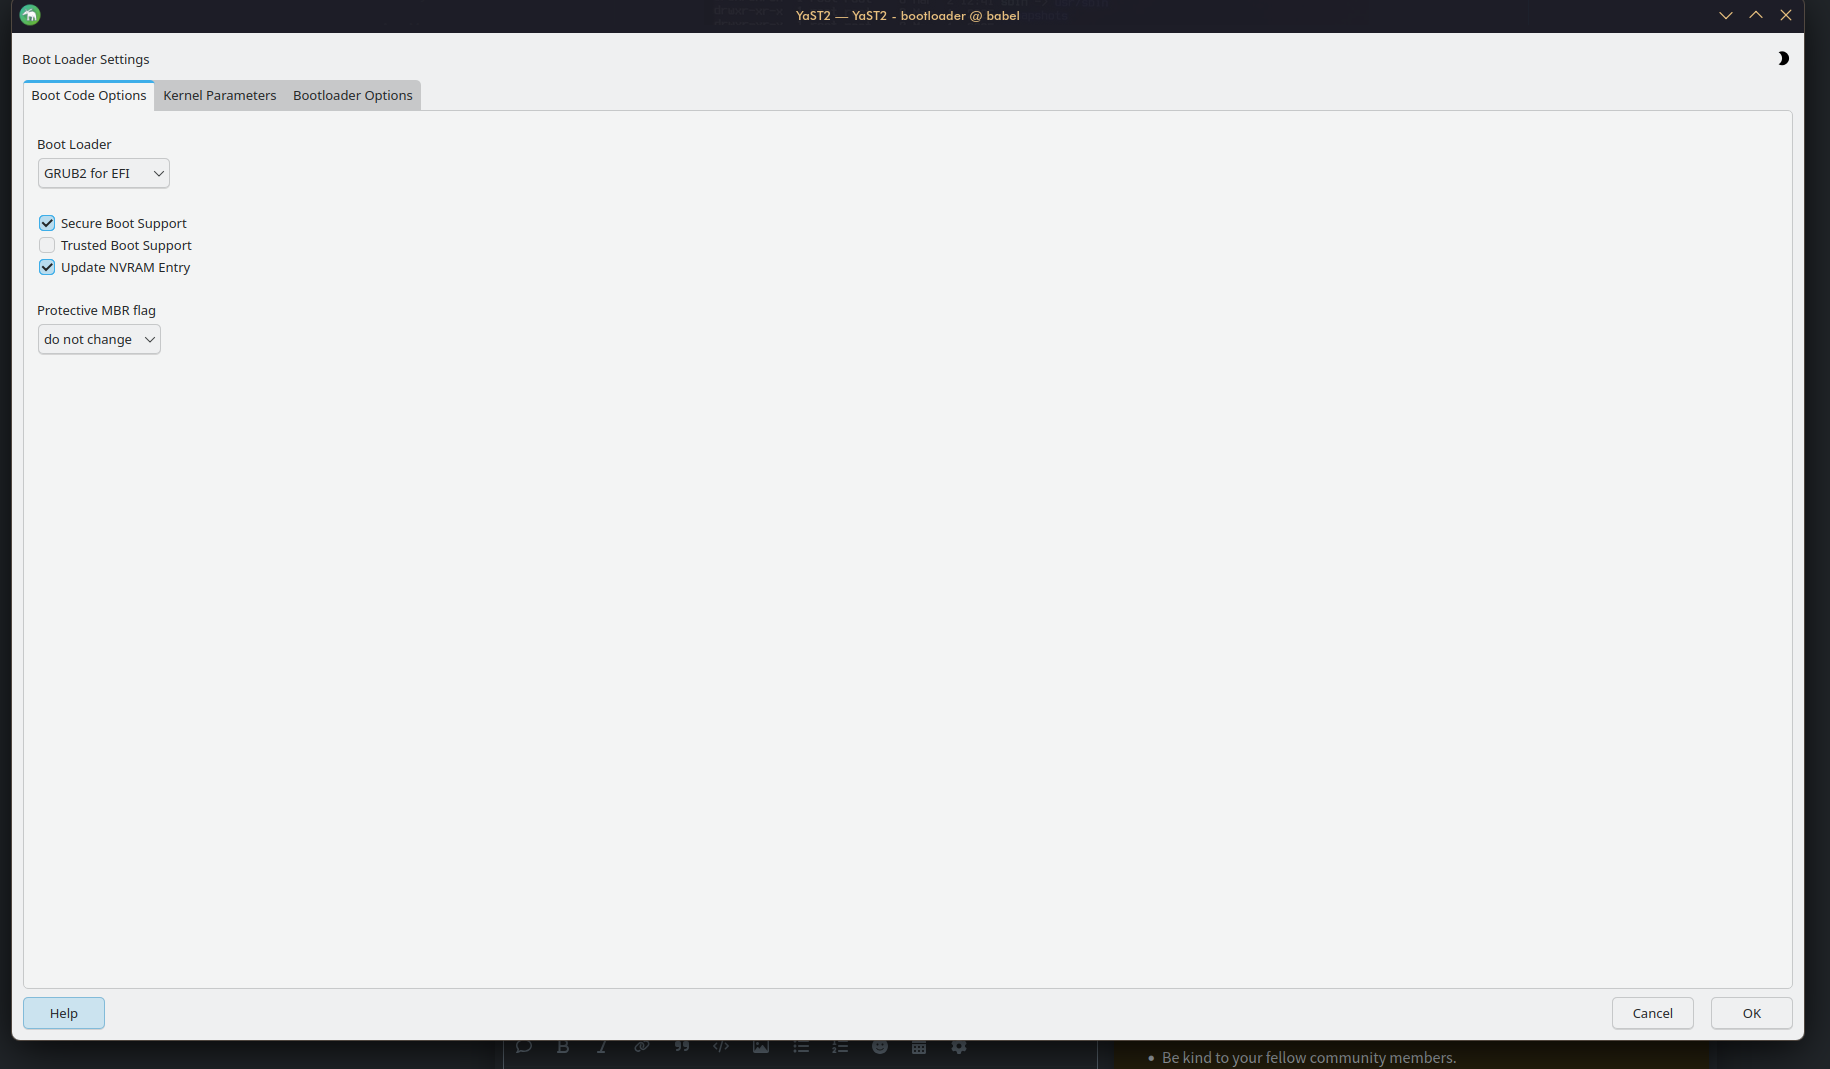
Maybe if you have a rescue USB you could see if you can get into YAST from that & open boot loader from the System menu in there that might be worth a try?
Or you can sudo yast from the rescue terminal, just in case using the USB puts the boot loader on there again. I was able to launch it in a terminal on a working system so maybe that might be a better way to try a YAST fix?
I assume you want Grub2 for EFI the drop down box there shows other options if you want them. You can also select or deselect Secure boot & trusted boot as you wish. Then maybe look at the bootloader options in the third tab, here you can change how many second Grub menu shows for & should have probe for foreign OS ticked which means it will find any other distros or windows & put them in the boot loader. When you are happy with your choices just hit the OK button & it should go off & work its magic. Then reboot with your fingers crossed.
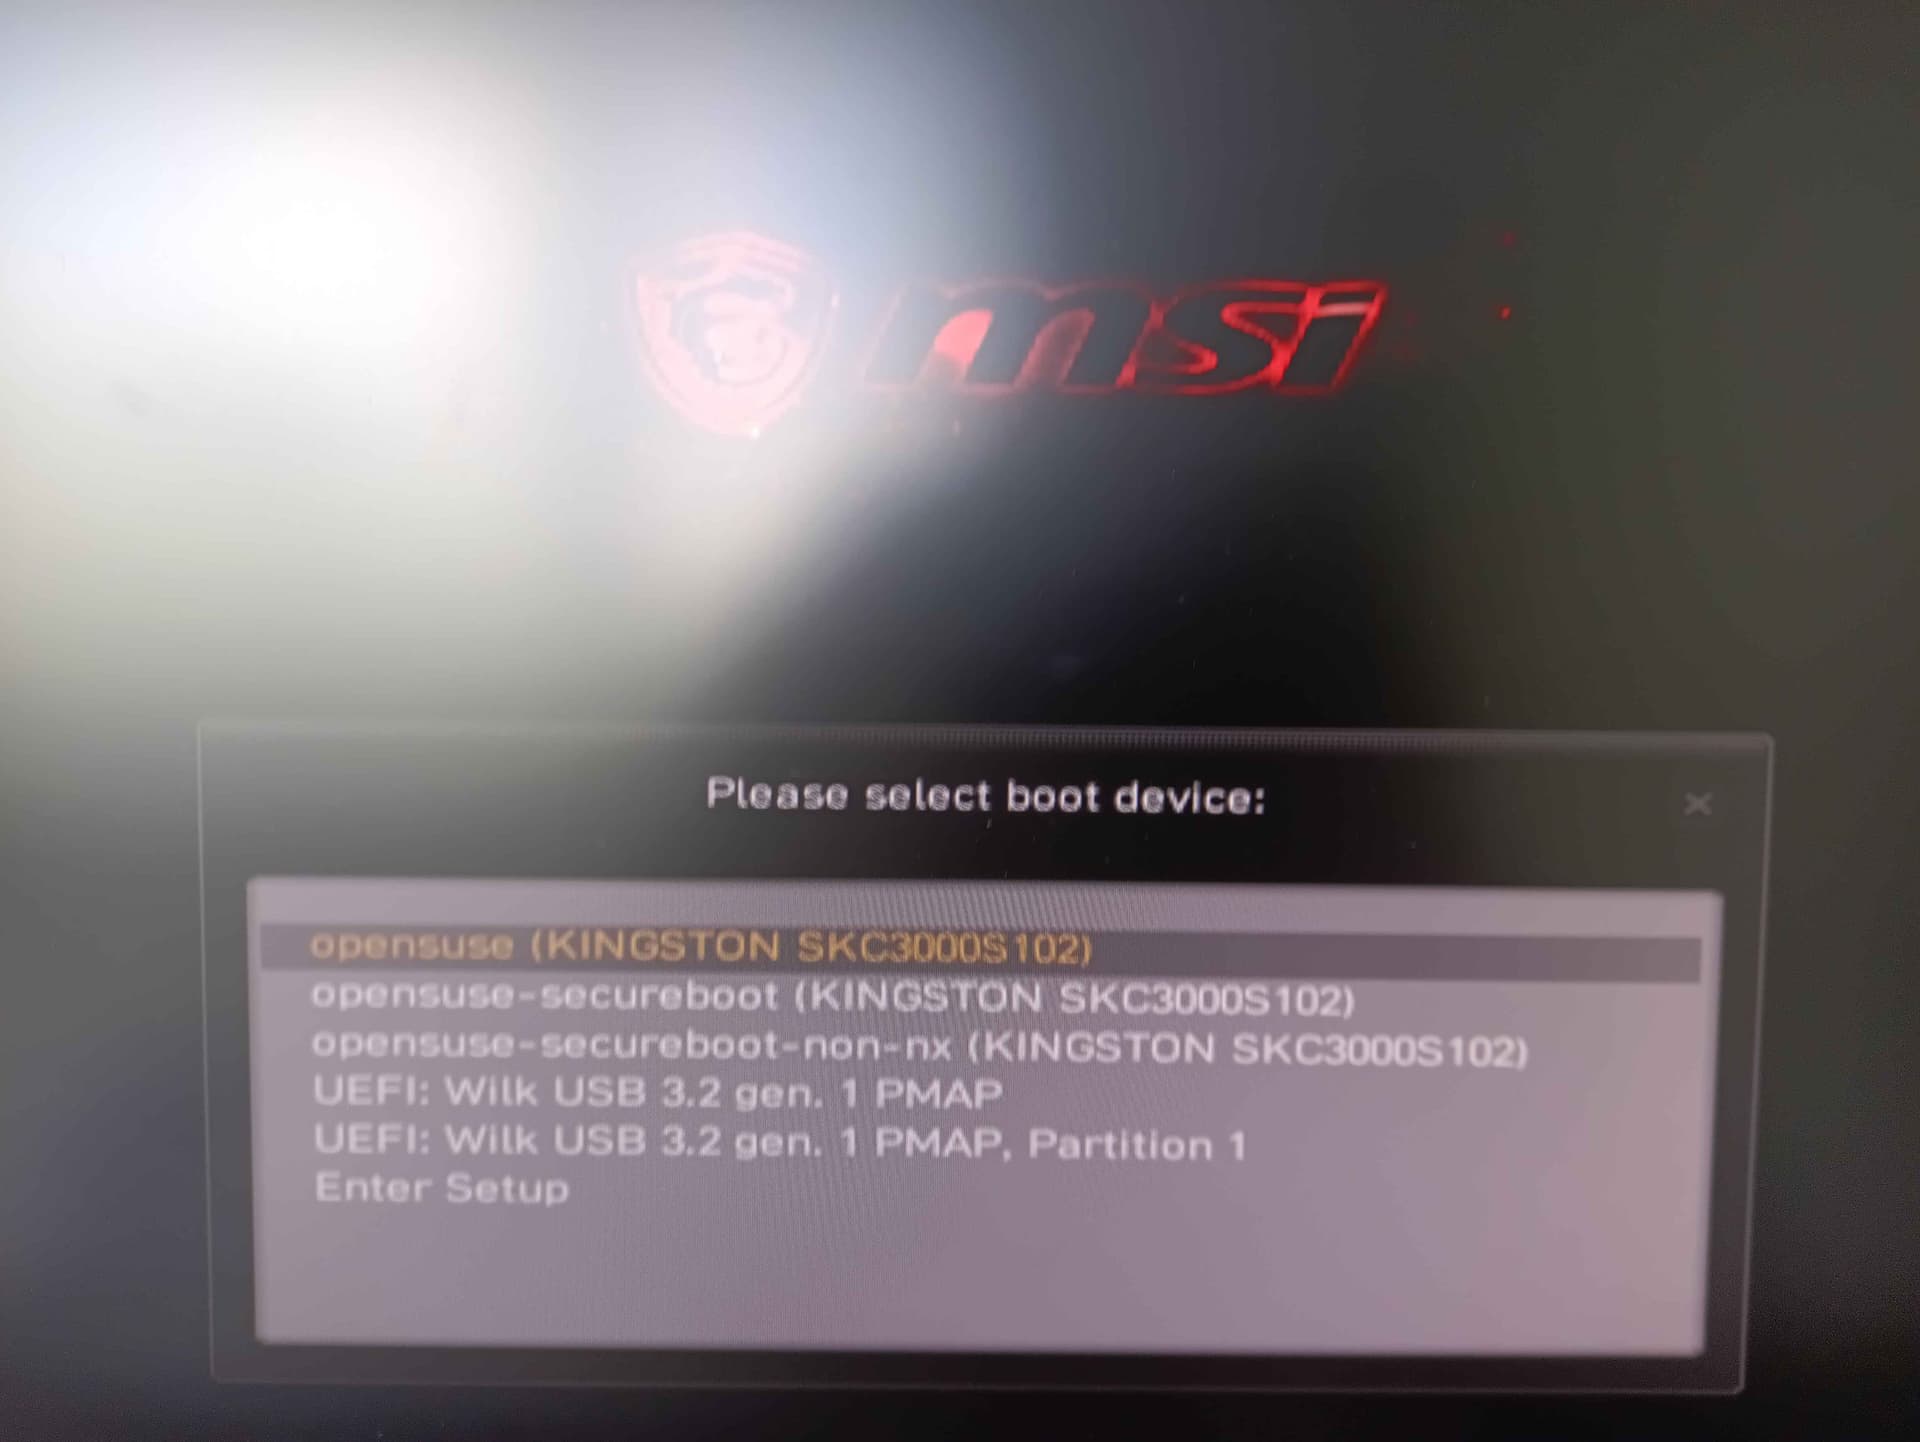
I can now boot without an USB, but the first one in the list (which is the default, throws me into grub rescue)
The second option works fine.
How can I clean up the load order/remove the broken first entry, so I wouldn’t need to hit F11 every time I boot?
Change it in the BIOS probably be the easiest - looks like you’re using MSI so here’s some info about that if you’re unsure about working with bios. Maybe make sure you know which disc or partition is which if they are different or just change the order in there. https://www.msi.com/support/technical_details/MB_Boot_Priority
Yeah, this worked. It boots from the working boot loader now. Thanks!
I do wonder what to do with the old broken boot loader. Will it cause problems later on if I leave it be? Can I remove that somehow?
Guess if you have moved it well down the list then it shouldn’t ever cause you any problems. But while you are familiar with finding your way round the BIOS there may well be an option to disable that one perhaps? But if ain’t broke now maybe don’t risk fixing it!
On older PC’s there’s various ways things can fail. From your screenshot I see basically 2 bootmethods: non-secure and secure, the 3rd option with suffix ‘non-nx’ I am not sure what that is. But those 3 entries are sort of URL’s that the tooling w.r.t . UEFI bootloader puts into the UEFI BIOS variable/data store. So not on SSD/HDD but in the motherboard flash chip.
I have had similar issues, at some point in time also an old laptop of mine that has Windows10, Tumbleweed, Debian on it, also got messed up w.r.t. that boot entries. I am not sure why, but Windows seemed to force SecureBoot at some point in time, maybe also Tumbleweed. So your first entry is non-secure and simply due to the now enabled SecureBoot, you cannot do non-secure boot.
The tool efibootmgr shows which entries are there, should match with the screenshot. efibootmgr -h shows also options to delete or re-order, just read carefully.
Then still, a big problem might be that there are bugs in the UEFI BIOS implementations, so if a efibootmgr action fails, you might end up with yet new problems. I have an old fanless Zotac AMD E-350 board that sort of randomly ‘forgets’ entries or efibootmgr says it cannot write to the motherboard flash storage.
On that old laptop also issue when it boots, but I am afraid that if I use efibootmgr to change something, that Windows does not want to boot (again) because it somehow finds that security is compromised or so. On newer but simple N100 minicomputer, it all works as expected and I can just use efibootmgr --bootnext 0003 to boot Debian once, where 0001 is Tumbleweed and 0002 is Windows Boot Manager.